Red-Blue Teaming Platform

Empower your enterprise with adversarial attack simulations and blue team defense validation. Execute live adversary emulation, test detection playbooks against MITRE ATT&CK techniques, and benchmark your SOC's incident response in a safe, isolated cyber range.

Adversarial Attack Simulation & SOC Defense Validation

Validate your organization’s cyber resilience through authentic Red vs Blue warfare and collaborative Purple Teaming exercises. Hacktify’s Red-Blue Teaming Platform bridges the gap between offensive realism and defensive readiness, allowing security teams to emulate sophisticated Advanced Persistent Threat (APT) campaigns, stress-test SIEM/EDR detection rules, and fortify enterprise incident response playbooks.

  • MITRE ATT&CK Aligned Scenarios: Realistic adversary emulation spanning initial access, lateral movement, privilege escalation, and exfiltration.
  • Real-Time Attack-Defense Telemetry: Measure blue team Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) against live offensive strikes.
  • Automated & Manual Campaign Execution: Run automated adversary emulation chains or conduct fully manual red team intrusions in isolated network environments.
  • Purple Teaming Collaboration Hub: Transparent exercise dashboards enabling red and blue teams to deconflict alerts, share IoCs, and optimize defenses in real time.

APT Adversary Emulation

Replicate state-sponsored and cybercrime tradecraft, customized malware execution, living-off-the-land techniques, and C2 infrastructure.

MTTD & MTTR Metrics

Granular analytics quantifying defense response times, missed detections, true positives, and security gap mitigation roadmaps.

Live SOC & EDR Validation

Test enterprise security controls against evasion tactics, obfuscated payloads, memory injection, and lateral Active Directory movements.

Enterprise-Grade Enclaves

Multi-tier isolated subnets with Domain Controllers, Linux servers, DMZ gateways, and simulated user activity.

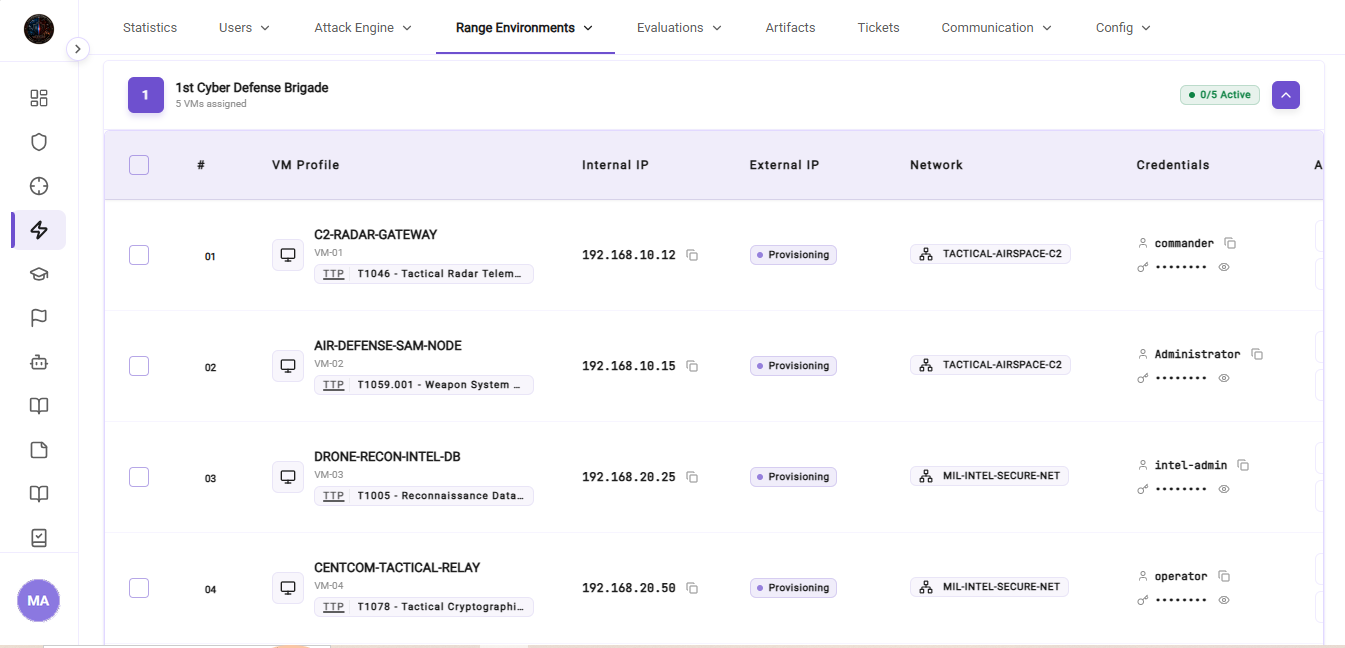
Hacktify Red-Blue Teaming VM Profiles and Provisioning Status
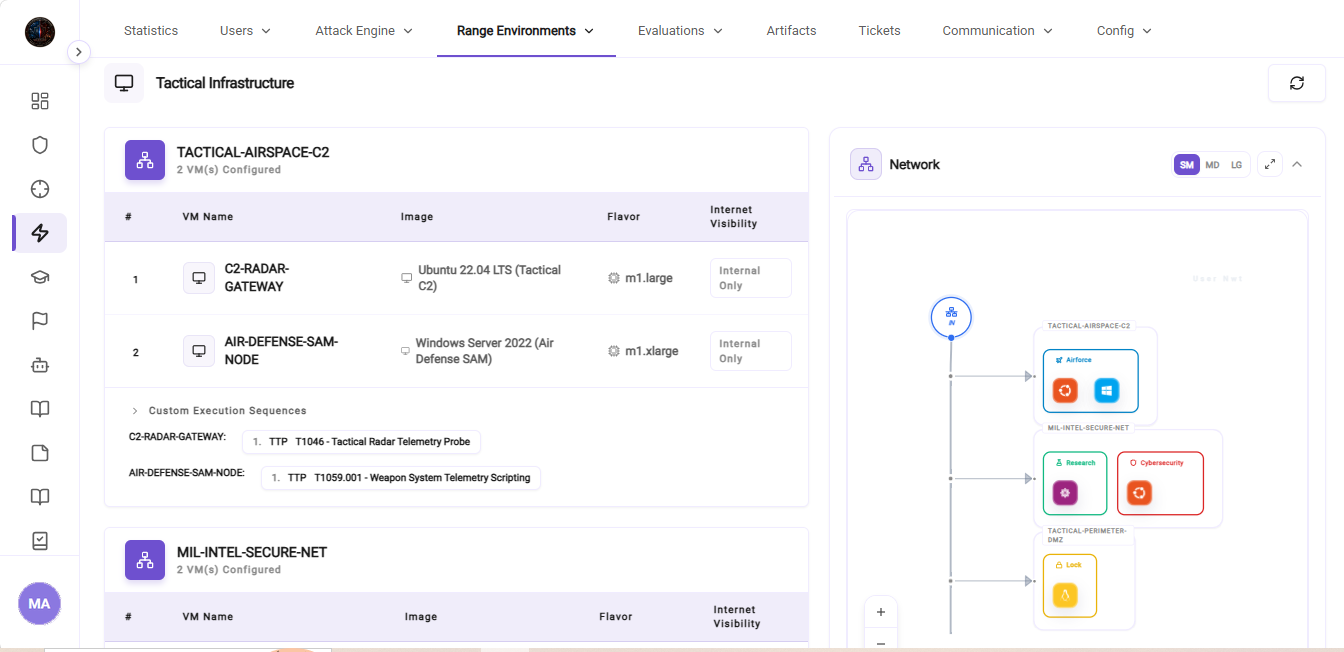
Hacktify Tactical Infrastructure Airspace C2 and Network Diagram
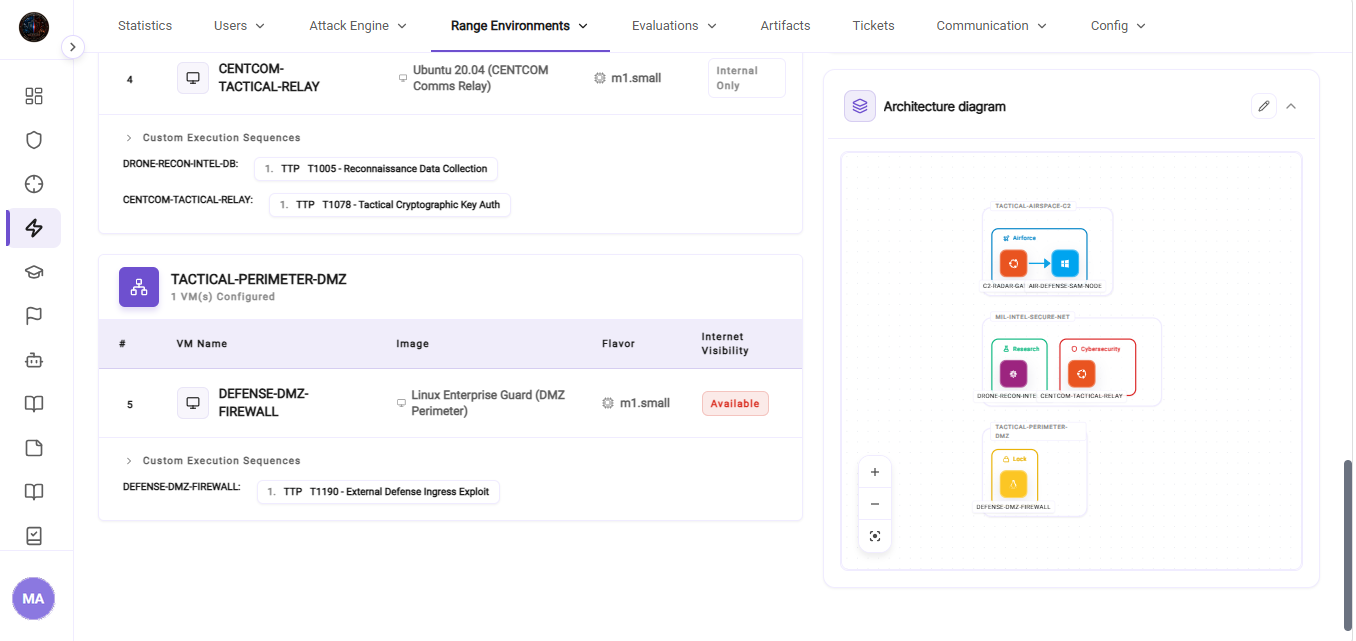
Hacktify Perimeter DMZ Firewall and Network Topology
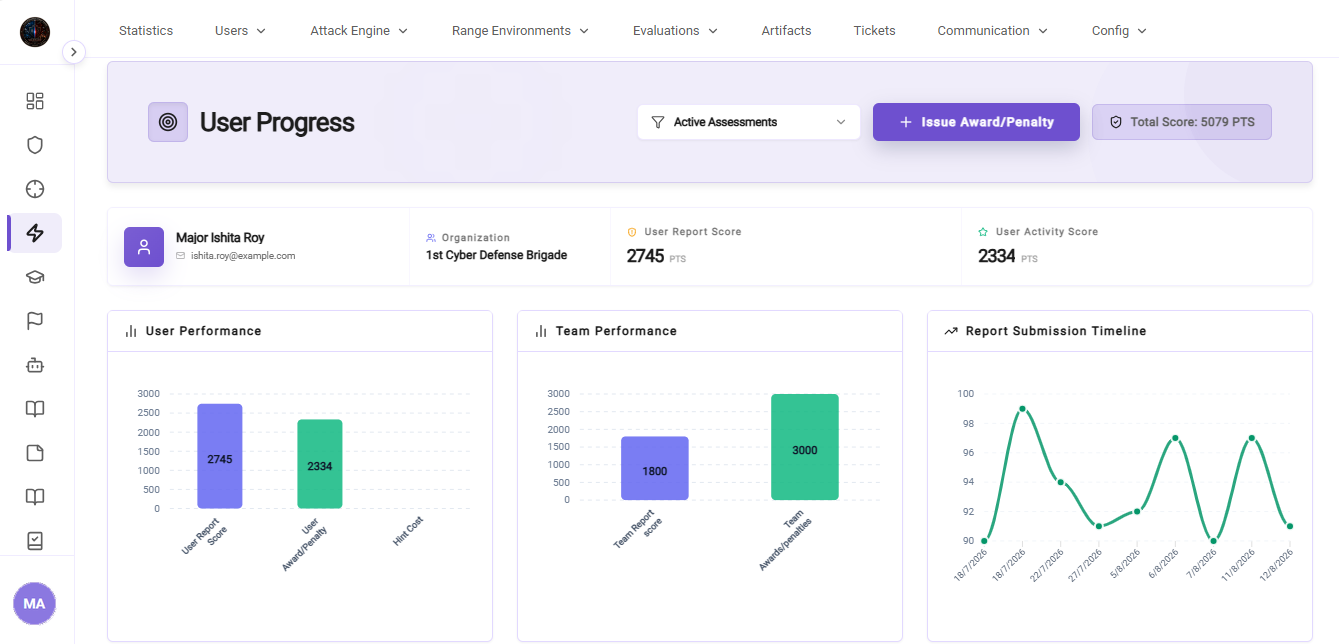
Hacktify Tactical Range User Score and Performance Analytics Dashboard

Bridge the Gap Between Offensive Impact and Defensive Readiness

Traditional vulnerability scans and tabletop reviews cannot prove if your SOC will detect an active adversary before domain dominance occurs. Hacktify’s Red-Blue Teaming Platform immerses defenders in high-tempo engagements where every alert matters. Validate your SIEM rules, test EDR containment workflows, and train analysts against unpredictable human attackers in controlled, high-fidelity corporate networks.

Multi-Vector Simulation Scenarios & Exercise Tracks

Curated offensive-defensive battlefields modeled after real-world breaches and modern enterprise threat vectors:

Active Directory & Domain Compromise

Kerberoasting, DCSync, pass-the-hash, domain trust exploitation, and BloodHound privilege escalation analysis against hardened forest architectures.

Command & Control (C2) & Lateral Movement

Adversary traffic simulation, covert DNS/HTTPS beacons, SMB named pipe pivot techniques, and internal firewall evasion.

Privilege Escalation & Defense Evasion

Kernel exploit mitigation, AMSI & ETW bypassing, token manipulation, and unquoted service path exploitation.

Ransomware & Destructive Attack Emulation

Emulate full-chain ransomware deployment, shadow copy destruction, multi-system encryption, and recovery playbook drills.

Cloud & Hybrid Identity Attacks

Azure AD/Entra ID token theft, AWS IAM privilege escalation, hybrid sync compromise, and cross-cloud persistence.

Threat Hunting & SOC Playbook Drills

Uncover hidden persistence mechanisms, hunt scheduled tasks, analyze memory artifacts, and optimize detection engineering rules.

Frontlines Says.

Reviewed on
4.9
Rated 4.5 out of 5
Contact us

Reach Us for Customized Platform Solutions

We’re happy to answer any questions you may have and help you determine which of our services best fit your needs.

Your benefits:
What happens next?
1

We Schedule a call at your convenience 

2

We do a discovery and consulting meting 

3

Set up Instance for you

Schedule a Free Consultation